More automated review comments do not necessarily mean better review. CodeRabbit’s funding announcement makes a useful occasion to separate activity from the defects a team actually catches.
Funding and product scope
In its August announcement, CodeRabbit reports $143 million raised at a $1.5 billion valuation, co-led by Atomico and Smash Capital. It introduces Triage for routing changes, Change Stack for explaining related modifications, and Security for examining shipped code. These are the company’s descriptions, not independent verification of detection performance.
The scope extends beyond commenting on a pull request. Prioritization asks which change deserves attention; explanation asks how its pieces relate; post-merge analysis asks whether the running codebase contains a reachable problem. A single count of reviews does not answer all three questions.
Twenty alerts can hide two different problems
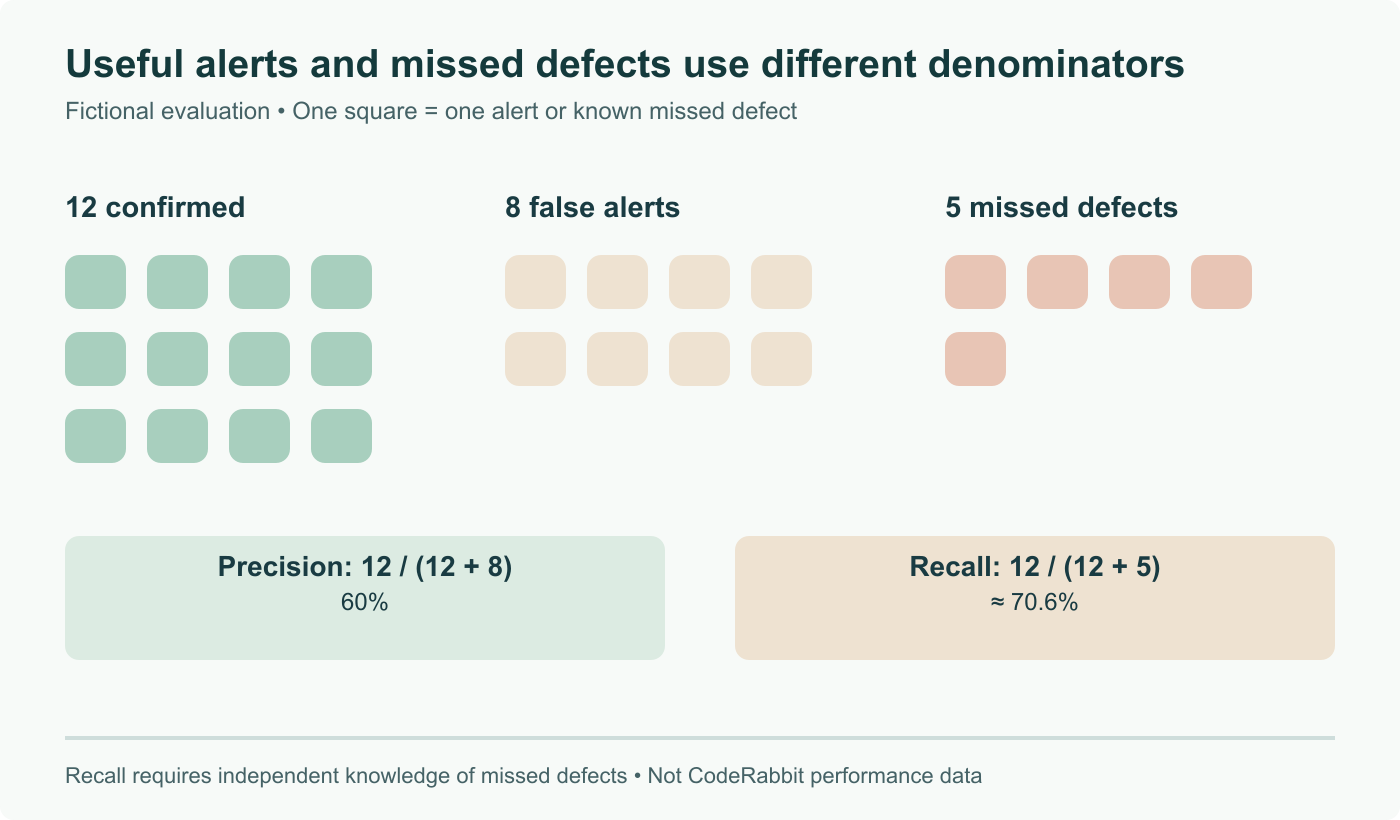
Our fictional evaluation produces 20 alerts. Manual adjudication confirms 12 defects and rejects eight alerts. Precision is 12 ÷ 20 = 60%: the share of reported findings that were useful in this example.
Suppose an independently checked test set contains five additional defects the reviewer missed. It then caught 12 of 17 known defects, giving recall of about 70.6%. This denominator requires knowledge of missed problems; it cannot be recovered from the tool’s own alert list alone.
The cover shows those three groups separately. Neither percentage is a CodeRabbit measurement. They explain why a product can post fewer comments while becoming more useful, or produce many comments while still overlooking serious failures.
Evaluate the decision the review supports
Use representative changes with known defects and sound changes that should pass. Classify findings by consequence: a cosmetic suggestion and a missed authorization check should not cancel each other out in an undifferentiated average. Record whether evidence is reproducible and how long a developer spends resolving each alert.
For triage, inspect whether a change touches a critical contract even when its diff is small. For post-merge security, confirm that a reported path is reachable in the deployed configuration. Keep the final release decision tied to evidence and ownership. Financing can support product development; it does not supply these evaluation results.
Attribute financing and product claims; replace review-volume quality inference with precision and missed-defect worked example.